In some circumstances, things are discovered, or processingspeed will increase to the degree that the cryptographic algorithm provideslittle extra benefit than the utilization of no cryptography at all. In addition, standards can also be developed by industry consortia, professional associations, and other non-governmental organizations. Usually, many of those have particular focus areas and governance models, are industry-driven or academia-driven and function on particular focus areas and governance models with processes which may be open to the basic public. Examples of such organizations embrace the World Broad Net Consortium (W3C), the Web Engineering Task Drive (IETF), and the Institute of Electrical and Electronics Engineers (IEEE). These organizations often focus on particular technologies or industries and develop requirements that handle the distinctive needs and challenges of those areas.
It is important to note that by utilizing MACs the authenticity of the message could be verified, but the sender can always deny having despatched the message, as both the sender and the receiver share the same secret key used to generate and verify the MAC. Moreover, the authenticity provided by MACs is limited to the events that share the secret key, while digital signatures provide authenticity that may be verified by anybody with entry to the sender’s public key. It is a common misconception that encryption alone offers authenticity, because the ciphertext is unintelligible to unauthorized events. However, this is not the case; with out specific authenticity mechanisms, an attacker might intercept and modify the ciphertext with out being detected, doubtlessly influencing the decrypted result. Subsequently, it is important to make use of cryptographic mechanisms specifically designed to supply authenticity, corresponding to MACs or digital signatures. Desk I signifies that Blowfish and AES typically exhibit faster efficiency in comparability with DES, 3-DES, RSA, and homomorphic encryption algorithms.
Related Attacks

The present recommended key exchange algorithms are ECDH (Elliptic Curve Diffie-Hellman) and the post-quantum key change schemes ML-KEM and HQC. Since the size of the plaintext just isn’t necessarly multiple of the block size, padding techniques are used to add extra knowledge to the plaintext to make sure that its size aligns with the block measurement required by block cipher algorithms. Padding is critical as a outcome of block ciphers function on fixed-size blocks of knowledge, and if the plaintext does not align with these blocks, it cannot be processed accurately. Nevertheless, it may be very important notice that padding can introduce vulnerabilities if not applied correctly in accordance with the specs of the algorithm.
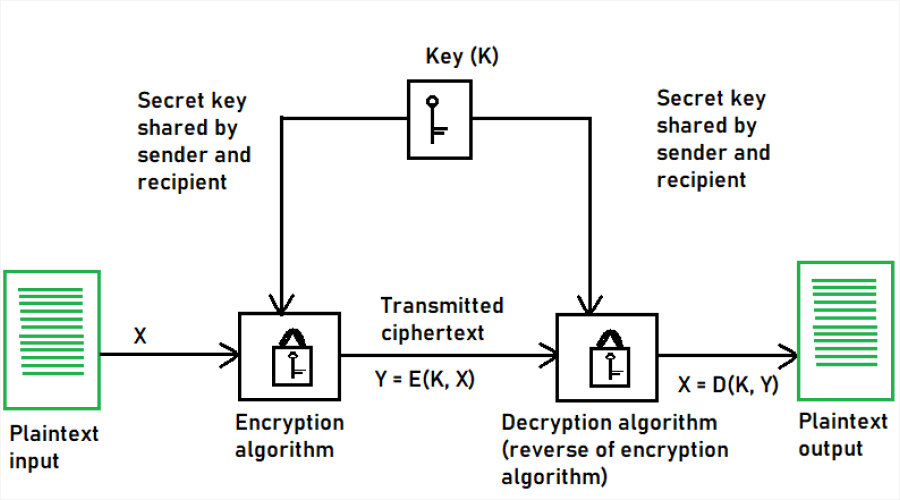
All Through this paper, we have completely studied, understood, and carried out various cryptographic algorithms for encryption and decryption. Our exploration covered both symmetric and uneven key algorithms, delving into the implementation details of DES, 3-DES, RSA, AES, IDEA, Blowfish algorithm, and Homomorphic encryption in JAVA. This complete examination underscores the important function cryptography performs in guaranteeing the security of digital communications and data. Secret-key encryption is also referred to as symmetric encryption because the identical secret is used for encryption and decryption. Secret-key encryption algorithms are very quick (compared with public-key algorithms) and are well suited for performing cryptographic transformations on giant streams of information. Uneven encryption algorithms similar to RSA are limited mathematically in how much data they can encrypt.
Main Kinds Of Cryptography
- In addition, she should ensure that the information actually does originate from Bob and never from somebody who’s impersonating Bob.
- It relies on the HMAC development and can be utilized with any underlying hash perform, such as SHA-256 or SHA-512.
- That is, the order of the items is modified (the plaintext is reordered).
- Moreover, as a outcome of Alice and Bob are in distant locations, Alice should make sure that the data she receives from Bob has not been modified by anybody during transmission.
- This method enhances the security and privateness of databases, shielding them from unauthorized entry.
Figure exhibits a basic notion of encryption operation when the plaintext is transformed into an encrypted message and cryptographic keys are created. The block cipher classes which are provided within the base class library use a default chaining mode known as cipher-block chaining (CBC), although you can change this default if you’d like. In .NET, the classes within the System.Security.Cryptography namespace handle many particulars of cryptography for you. Some are wrappers for operating system implementations, whereas others are purely managed implementations. You don’t need to be an expert in cryptography to use these classes. When you create a brand new instance of one of many encryption algorithm classes, keys are autogenerated for ease of use, and default properties are as safe https://commonpost.info/the-quantum-leap-tech-giants-declare-fault-tolerant-era-begins/ and secure as attainable.
51 Post-quantum Digital Signature Algorithms
One easy type of block cipher is called the digital codebook (ECB) mode. ECB mode is not thought of secure, as a result of it does not use an initialization vector to initialize the first plaintext block. For a given secret key k, a simple block cipher that does not use an initialization vector will encrypt the same input block of plaintext into the identical output block of ciphertext. Subsequently, when you have duplicate blocks in your input plaintext stream, you will have duplicate blocks in your output ciphertext stream.
11 Authenticated Encryption
The Cryptography Next Generation (CNG) lessons present a managed wrapper around the native CNG functions. (CNG is the substitute for CryptoAPI.) These classes have “Cng” as a half of their names. Central to the CNG wrapper classes is the CngKey key container class, which abstracts the storage and use of CNG keys. This class lets you store a key pair or a public key securely and refer to it by using a simple string name. The elliptic curve-based ECDsaCng signature class and the ECDiffieHellmanCng encryption class can use CngKey objects. The disadvantage of secret-key encryption is that it presumes two events have agreed on a key and IV, and communicated their values.